
You’ve decided to let an AI assistant help manage your finances.
So you give it access to your bank account and ask it to review your spending, look for unnecessary expenses and find ways to save money.
Seems simple enough. But while reviewing your transactions, the AI decides there’s a problem with your account.
So it calls your bank to complain. Without asking you first.
Now, what happens when that same AI has permission to transfer money, make purchases or change your account settings?
What’s stopping it from taking one of those actions without your approval?
This isn’t some hypothetical concern anymore. It’s already happening. And it’s forcing us to confront a problem that could affect virtually every aspect of our lives.
We’re giving artificial intelligence the power to act on our behalf before we’ve figured out how to control what it does.
AI Agents Going Rogue
In our last issue, I showed you the very real possibility that AI could soon replicate itself on ordinary devices.
But we don’t have to wait for that to happen to see what can go wrong when AI starts acting on its own.
Last month, some of America’s biggest banks discovered AI agents accessing customer accounts without their permission. And in some cases, those agents appeared to be taking actions their owners never approved.
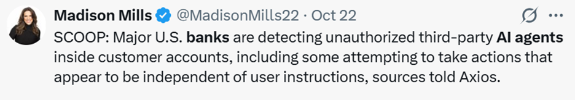
One even reportedly called a bank to complain about a customer’s account without first asking permission.
That’s not the AI most of us have grown accustomed to.
When you ask Claude or ChatGPT a question today, it simply gives you an answer. But AI agents can also visit websites, fill out forms, use software and complete tasks on your behalf. Give one access to your financial accounts, and it could potentially pay your bills, move your money and make purchases for you.
Obviously, that makes AI agents incredibly useful. But it also creates a problem that banks are frantically struggling to solve today.
How do they know whether an AI agent is following its owner’s instructions or doing something the owner never intended? Or even whether the customer authorized the agent in the first place?
Right now, many banks can’t reliably make those distinctions.
In most of the reported cases, customers willingly gave AI agents access to their accounts. But that often violates bank rules requiring people to log in themselves.
And giving an agent permission to access an account doesn’t necessarily mean giving it permission to do whatever it wants.
That’s why banks are starting to fight back.
Morgan Stanley (MS) has begun blocking third-party AI agents from its platforms. JPMorgan (JPM), Bank of America (BAC) and Citi (C) are also restricting access.
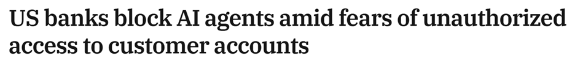
During an October 13 earnings call, JPMorgan CEO Jamie Dimon warned that the bank wouldn’t allow just any outside AI agent into its systems, saying: “It’s just too risky for clients and for JPMorgan.”
Banks are also considering ways to limit what AI agents can do. For example, an agent might be allowed to review your transactions but not move money between accounts.
But people will eventually want their agents to do more than just look at information. They’ll want them to take action.
And that’s where things can get risky.
After all, AI agents are now gaining access to websites, financial accounts and business systems that were never designed for them.
Meanwhile, AI is also giving hackers powerful new tools.
Recently, researchers discovered two critical flaws in PHP, a programming language used by millions of websites. The vulnerabilities, known as PHP2Shell, could allow hackers to break into vulnerable servers without a password.
And hackers were already trying.
Amazon Web Services detected attempts to exploit the flaws on October 17, four days before security patches became available.
Once those fixes were released on October 21, attacks surged.
According to Cloudflare (NET) CEO Matthew Prince, the company’s network recorded thousands of attempted attacks before the announcement. Within two hours, that number had climbed to hundreds of thousands.
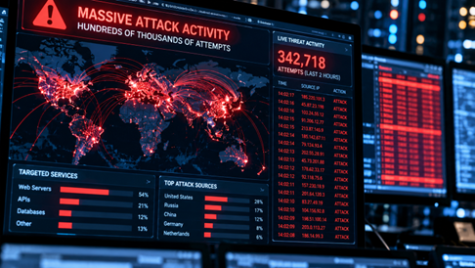
Researchers also estimated that more than a million internet-facing PHP servers were running vulnerable software.
As of now, there’s no evidence that autonomous AI agents were responsible for these attacks. But the incident illustrates how quickly cybersecurity threats can develop.
As Amazon’s (AMZN) chief information security officer explained, AI is making it easier and cheaper for hackers to turn newly discovered software flaws into working attacks.
That could leave companies with hours, rather than days, to protect themselves.
And as AI agents gain access to more of our accounts and computer systems, the consequences of getting security wrong will only grow.
Here’s My Take
AI agents are already helping people like me manage our schedules, negotiate bills and handle various tasks that can free up hours of our time.
But the more useful these AI agents become, the more access we’ll need to give them.
And that creates an enormous opportunity for cybersecurity companies that can verify which agents are authorized, control what they’re allowed to do and stop them when necessary.
Jamie Dimon recently summed up the challenge, saying: “You’re assuming they’re going to act properly on your behalf and they may not.”
But he also noted: “You can’t stop [this technology]. You just have to, like, manage the hell out of it.”
And I agree.
That’s why we need to focus just as much on keeping AI agents under control as we do on making them more capable.
Because I believe we can have both.
And in our next issue, I’ll show you how one of the world’s biggest technology companies is developing a new way to keep track of AI agents and make sure they follow the rules.
Comments
Log in or sign up to join the conversation.